Sales Compensation Software Benchmark
Download

Security and compliance
you can verify

Qobra runs on your most sensitive data: pay, quotas and performance. That's why commission software security comes first: SOC 2 Type II, GDPR, EU or US hosting, and a public Trust Center where you can check every control for yourself.

Rated 4.8/5 with 1,000+ reviews

Silver circular emblem with the text 'AICPA SOC 2 Type II Certified SAS 70 Reviewed' around the edges.
SOC 2 Type II
Certified Security
The acronym GDPR in bold black letters surrounded by a circle of 12 black stars, symbolizing the European Union's General Data Protection Regulation.
GDPR
EU Data Privacy
Black and white graphic with the words 'SECURITY AUDIT' above a checkmark and magnifying glass symbol.
Vaadata Audited
Annual Pentest
AWS logo with lowercase letters and an orange curved arrow underneath.
AWS Hosting
EU or US Region

How we protect your commission data

Encrypted, and locked down by default.

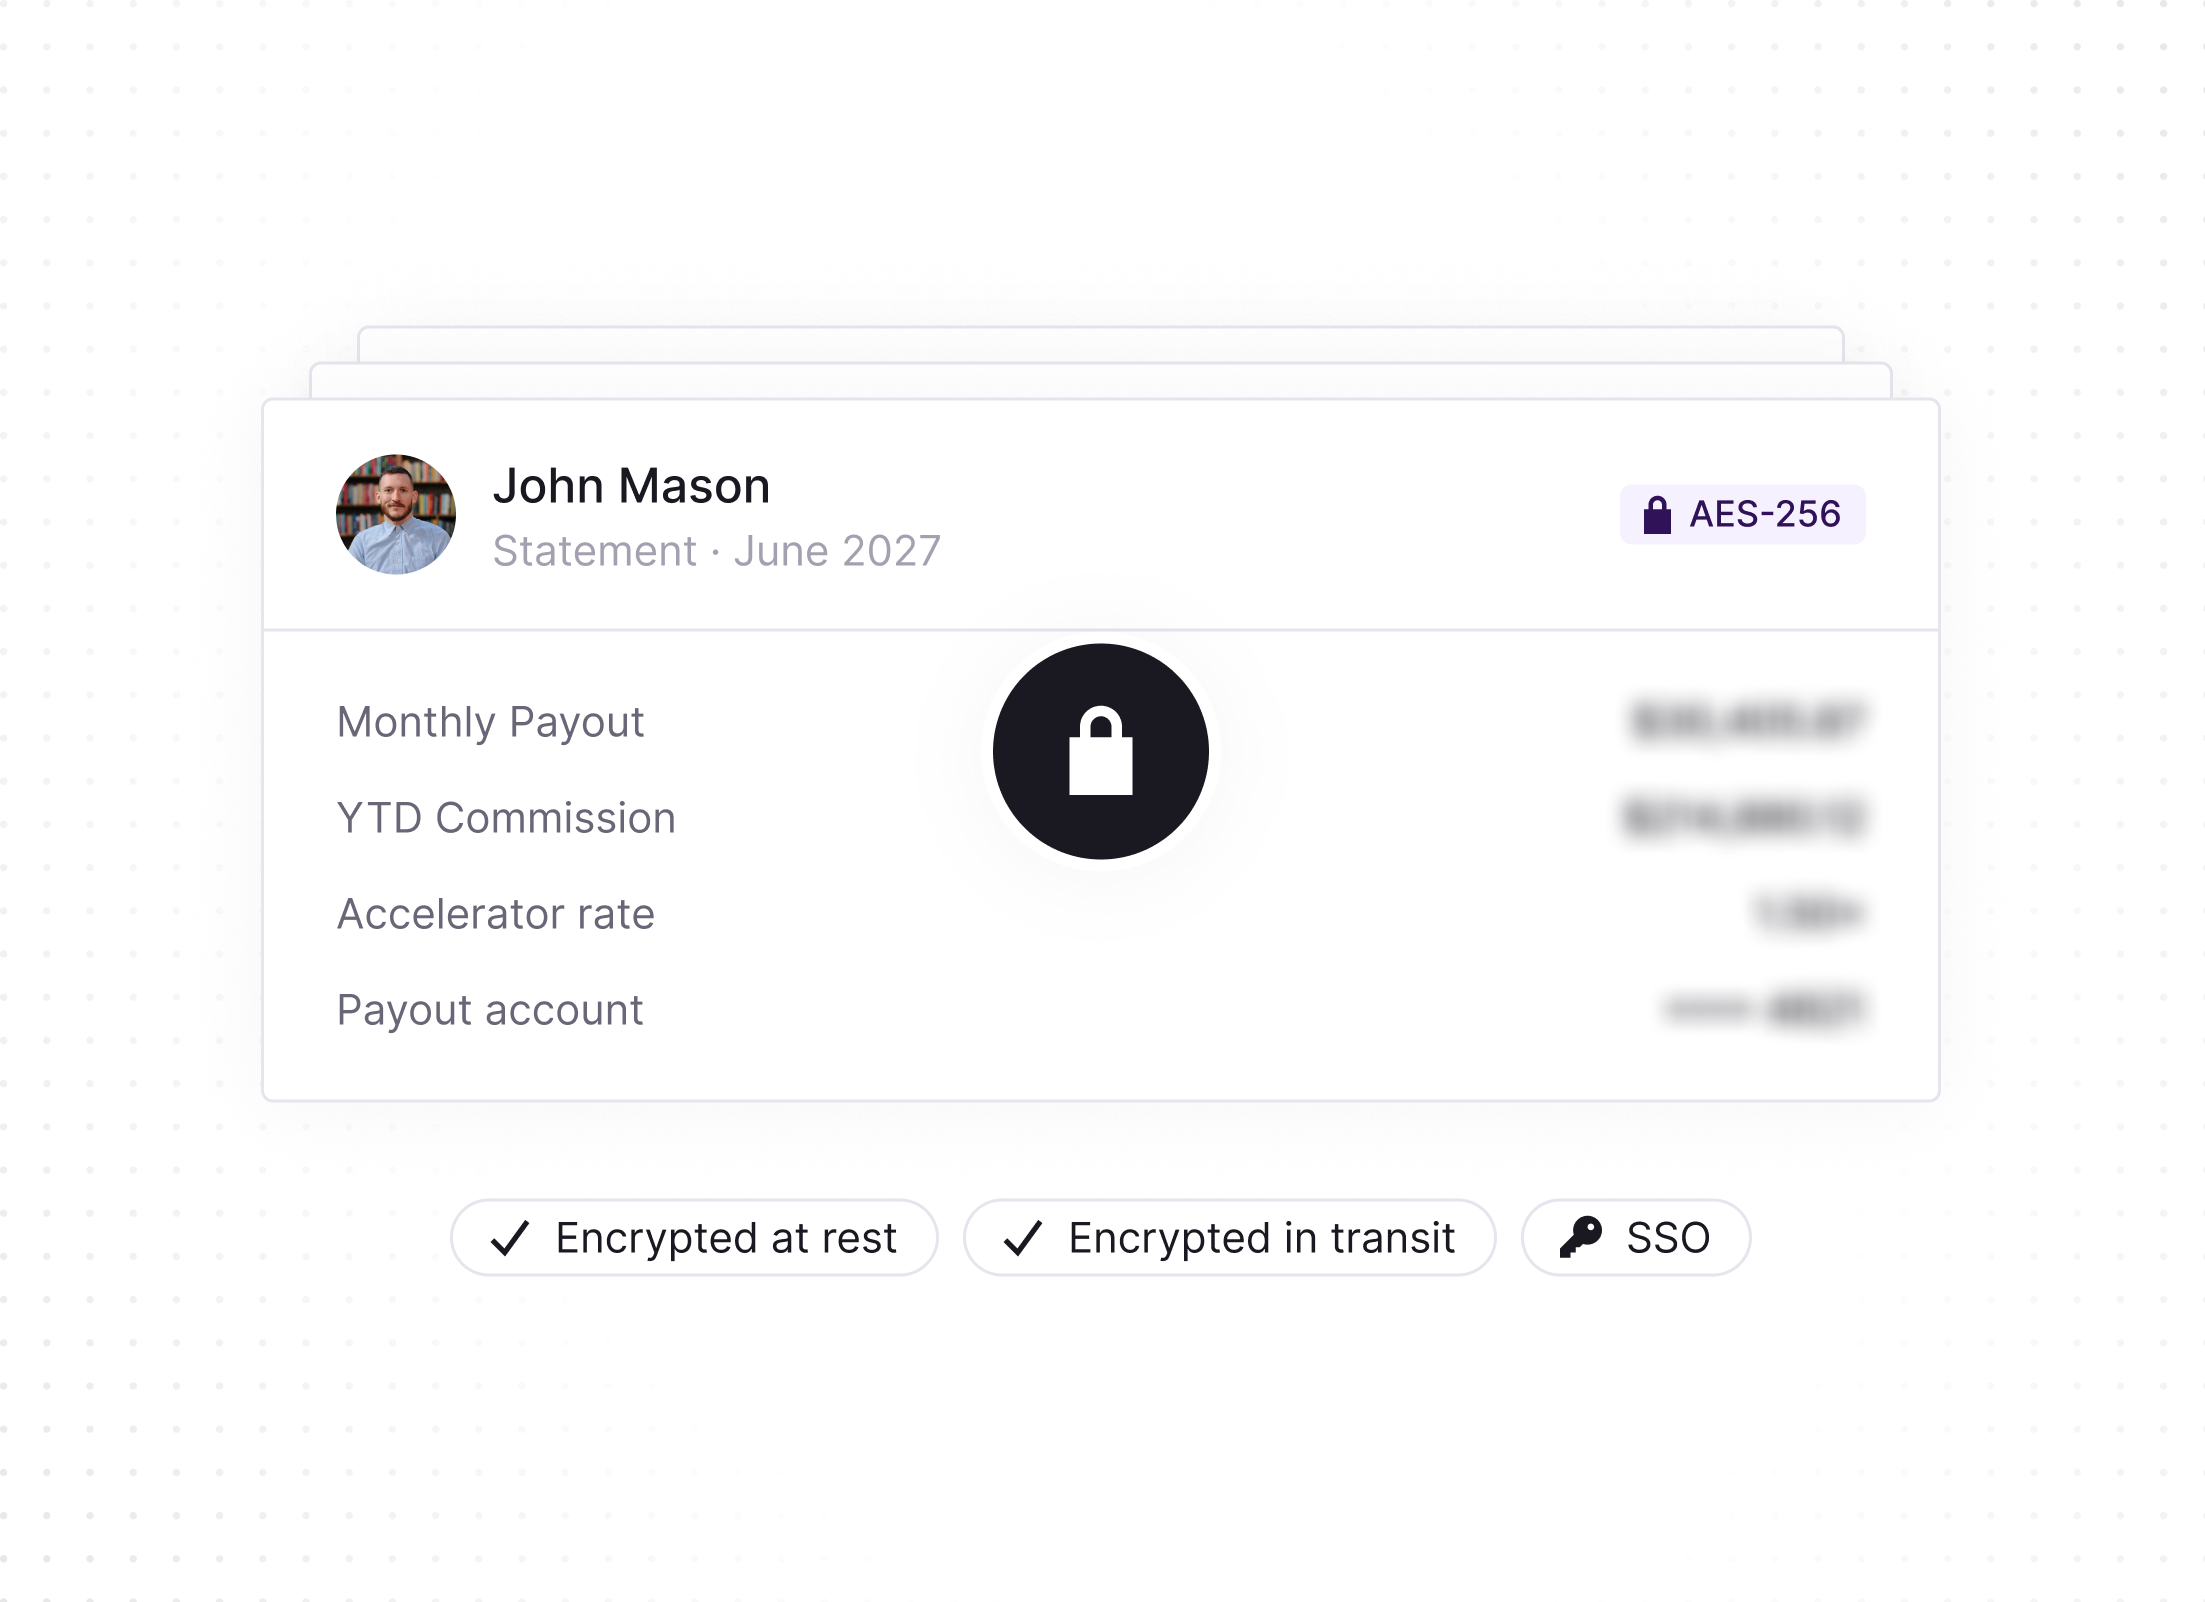
Customer data encrypted with AES-256 at rest and TLS 1.3 in transit

Production access restricted to authorized engineers, behind VPN and MFA, reviewed every quarter

SAML 2.0 SSO (Scale plan), Google sign-in, and a 14-character minimum password policy

Access revoked on termination through a checklist, within a defined SLA

Digital statement for John Mason dated June 2027 showing monthly payout, year-to-date commission, accelerator rate, and payout account details obscured by a lock icon signaling encryption with AES-256 security, accompanied by badges indicating data is encrypted at rest, encrypted in transit, and supports single sign-on.

Your data is hosted in the EU or the US.

Hosted on AWS, in the EU or in the US, you choose

Every sub-processor published, with its role and its region

Data Processing Agreement available to every customer

Free self-service export, then full deletion within 60 days of contract end (or earlier on request)

AI runs on Amazon Bedrock within your geography (EU or US), prompts are never shared with the model provider

Dot map of the world highlighting two AWS data regions: US N. Virginia (us-east-1) and EU Paris (eu-west-3), both marked with check icons. Labels below indicate Hosted on AWS, Sub-processors published, and DPA available.

Everyone sees exactly what they should.

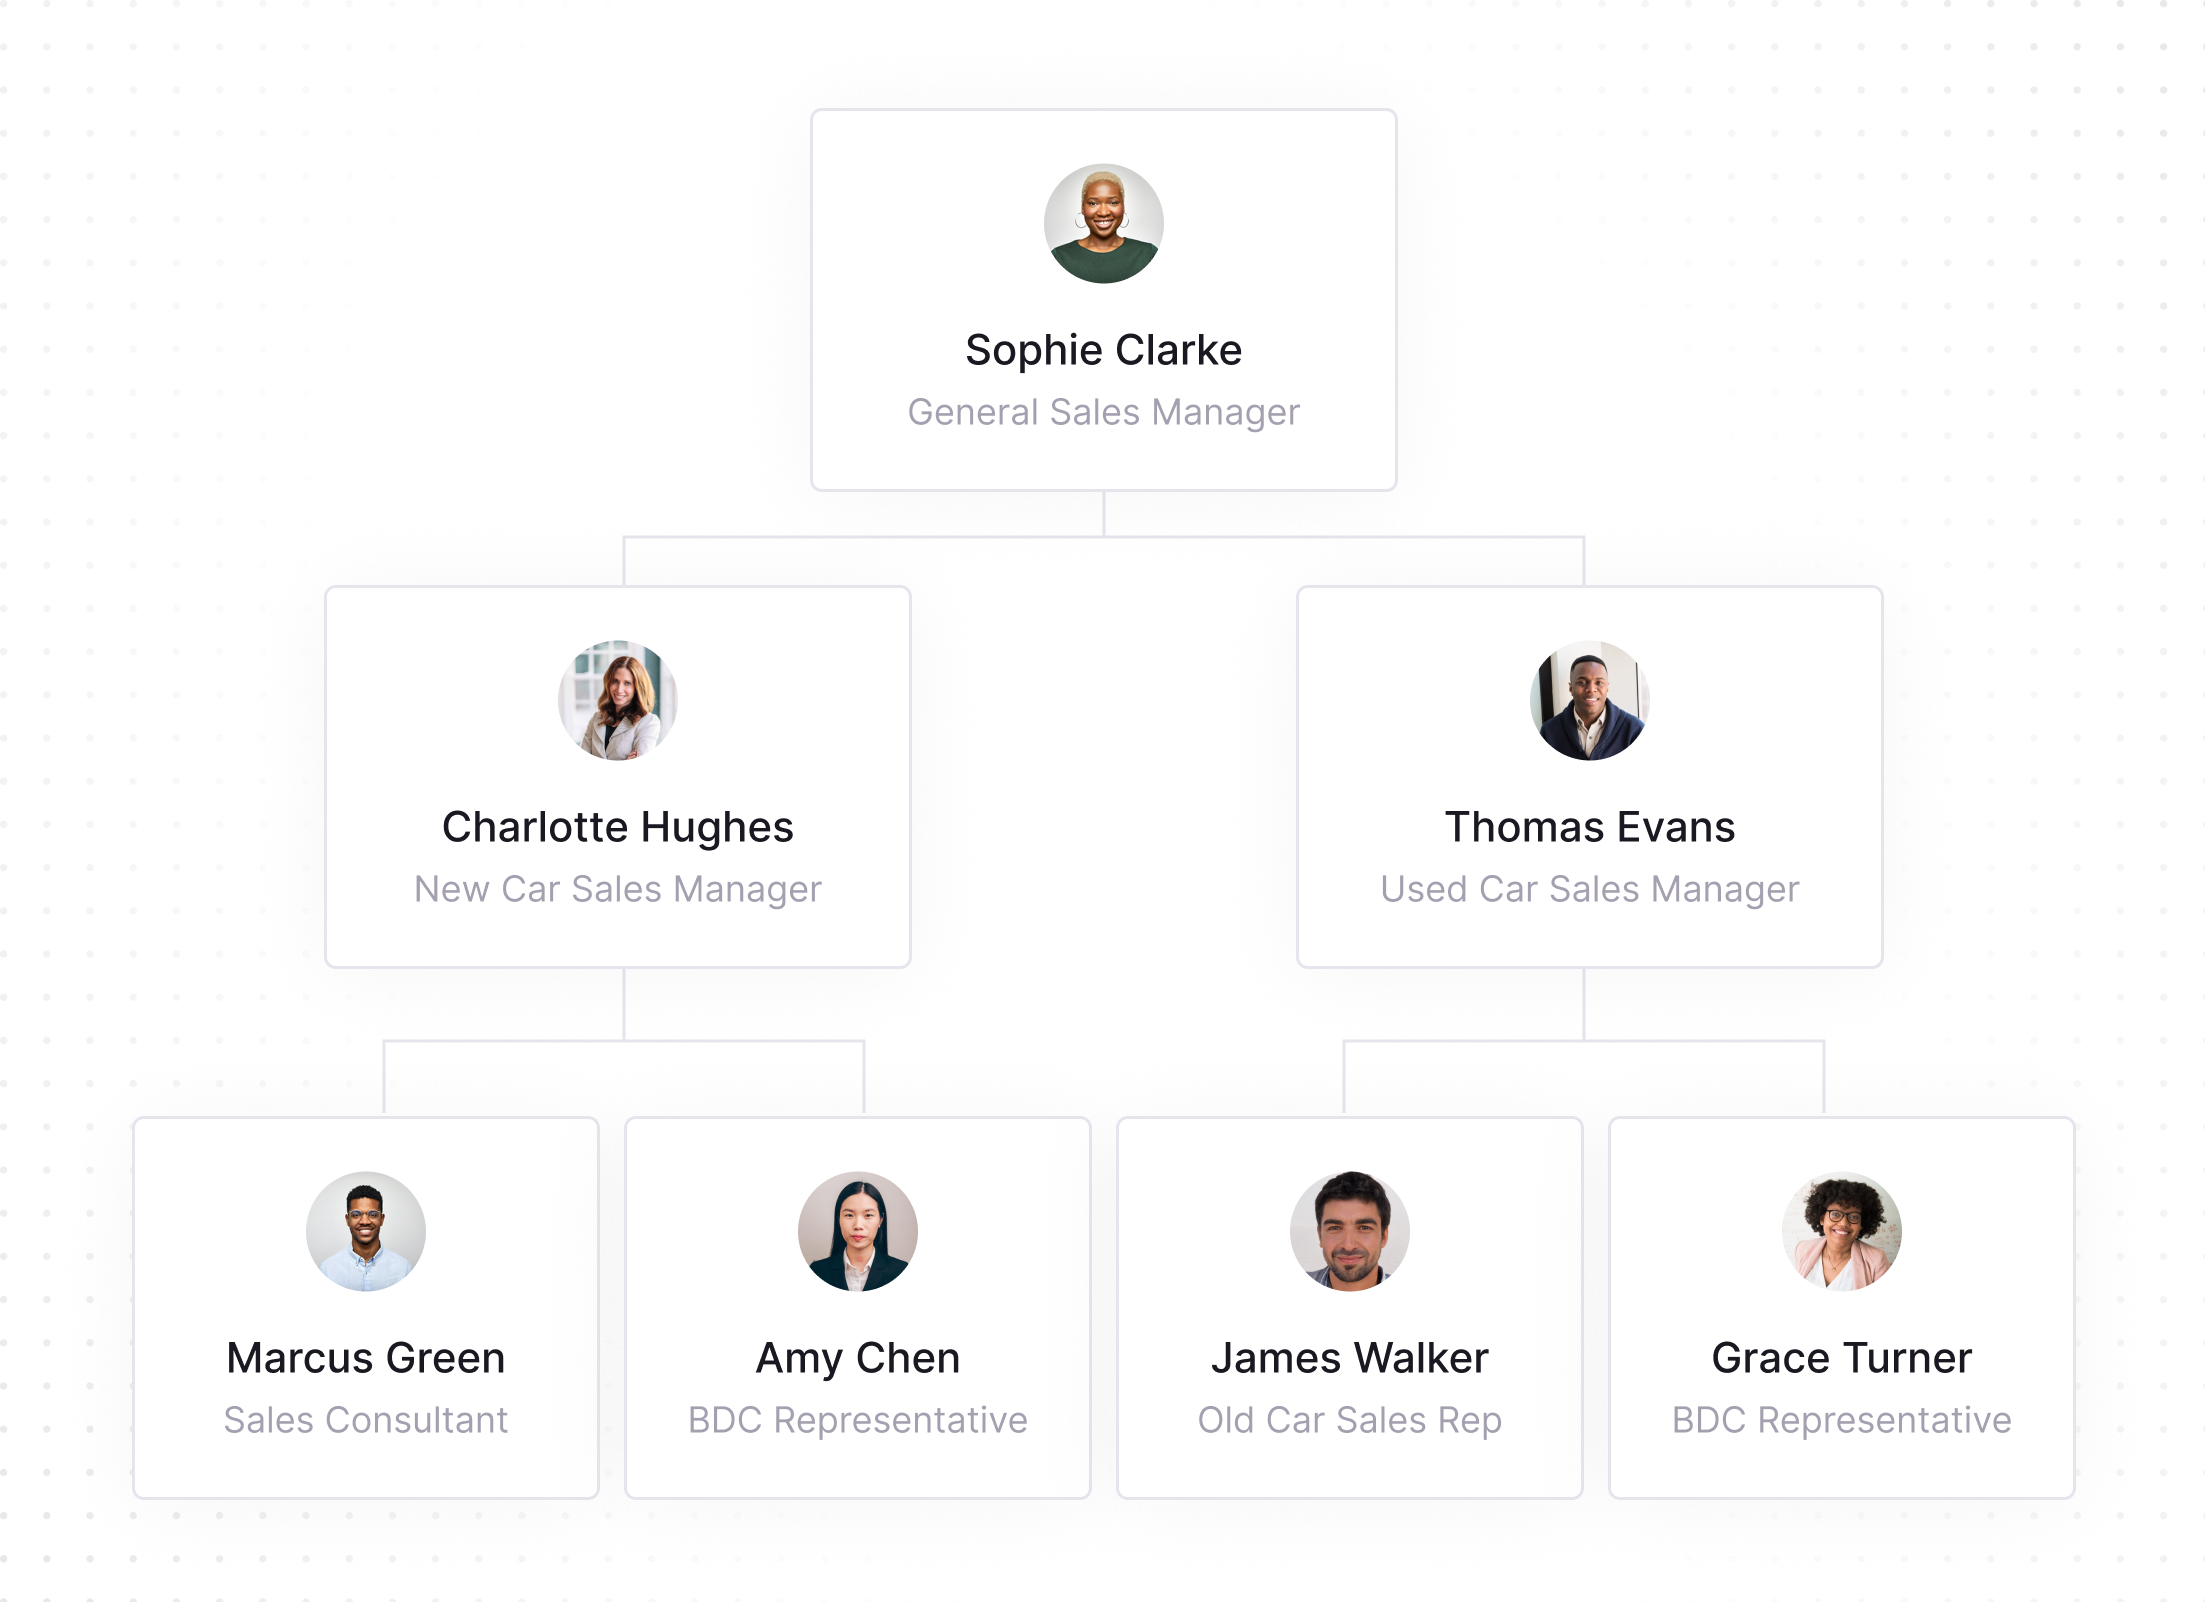
Granular role-based access: reps, managers, finance and admins each see only what their role allows

Custom validation workflows and approval chains

Complete audit trail on every change, with full traceability for your auditors (available on selected plans)

Organizational chart with Sophie Clarke as General Sales Manager at the top, overseeing Charlotte Hughes (New Car Sales Manager) and Thomas Evans (Used Car Sales Manager). Charlotte manages Marcus Green (Sales Consultant) and Amy Chen (BDC Representative). Thomas manages James Walker (Old Car Sales Rep) and Grace Turner (BDC Representative). Each person is shown with a circular headshot above their name and title.

Built to keep running.

Disaster recovery tested every quarter, RTO under 24h, RPO 24h, within our SOC 2 scope

Daily encrypted backups, stored in a separate availability zone in your region

Security vulnerabilities fixed within 48h (critical) and 7 days (high), with continuous monitoring and formal change management

Graphic with a shield in the center displaying the word 'qobra' and three text labels around it: 'BCP & DRP tested yearly' with a shield icon, 'Encrypted backups' with a database icon, and '24/7 monitoring' with a heartbeat icon, representing security features.

AI you stay in control of

Your data is never used to train models.

Your commission data, your plans and your conversations with Qobra AI stay yours. They are never used to train, fine-tune or improve any AI model (ours or a third party's) and never shared with other customers. Models run on Amazon Bedrock within your geography, and prompts are never shared with the model provider.

AI inherits your permissions, never bypasses them.

If a user cannot see a statement, a plan or a record in Qobra, no agent can see it either. The same goes for the AI tools you connect through our MCP server: off by default, authenticated with OAuth 2.1, and bound to the exact same permissions on every call. Whatever an agent does, it does as the user, never beyond their rights.

On or off, your call.

You decide. Admins can switch any agent, or all AI, on or off at any time, with a single toggle. No agent ever acts on its own: nothing it prepares takes effect until a user confirms it. Every AI interaction is identified and logged, in line with the GDPR and the EU AI Act transparency requirements.

Security is a daily practice, not a yearly audit

Geometric design with a central cluster of small orange dots surrounded symmetrically by larger circles in orange, purple, and yellow gradient colors arranged in a star-like pattern.
75+
Security controls continuously monitored across infrastructure, product, organization, internal procedures and data privacy, with live status published in our Trust Center.
Abstract geometric pattern of concentric circles and dots arranged in a diamond shape with gradient colors transitioning from purple in the center to cream and orange on the outer edges.
0
Critical vulnerabilities found in 5 years of independent white-box pentests (2022 to 2026), and every finding tracked to remediation under strict deadlines.
Circular arrangement of small to medium gradient circles in orange and purple hues forming a ring-like pattern.
0
Data breaches since Qobra was founded in 2020.

Don't take our word for it

SOC 2 Type II reports, pentest reports and remediation plans, insurance certificates, our Quality & Security Assurance Plan, the sub-processing register and the live status of every control. Request access and get the full picture in a few clicks.
dots
01
02
03
04
White stylized letter G with a superscript 2 inside a solid orange circle.
4.8/5
with 1,000+ reviews
View all customer stories
“I would say the tooling is very simple. You can see where the variables are coming from, so it was very easy and quick for our team.”
Jessica Ho, RevOps Manager at ElevenLabs
Watch the ElevenLabs story
“Since we’ve had Qobra, we’ve seen between 15 and 20% progress towards our objectives.”
Fabian Q. Veit, CEO at Make
Watch the Make story
“It’s more the fact that I just don’t have to worry about commissions anymore.”
Chris Cook, RevOps Director at GoCardless
Watch the GoCardless story
“At the end of every period, when we run commissions right now, we do a simple check with our finance team, and that’s it.”
Derek Boelig, VP RevOps at DataSnipper
Watch the DataSnipper story

FAQ - Security and compliance

Yes. Qobra has been SOC 2 Type II audited every year since 2024 by an independent firm. The latest report is available on request through our Trust Center, along with the scope of the audit. Our first SOC 1 Type II audit is also underway.

On AWS, in the EU (app.qobra.co) or in the US (app-us.qobra.co). You choose your region when your workspace is set up. Every sub-processor we use is published in our Trust Center with its purpose and its region.

Yes. Qobra acts as a data processor. We provide a standard DPA, publish our sub-processors, have an external DPO, and notify customers within 24 hours of identifying a data breach. Your data is deleted within 60 days of contract end, or earlier on request.

Only the people you decide. Access is role-based: reps see their own statements, managers see their team, finance and admins see what their role allows. Validation workflows and a complete audit trail keep every change traceable.

No. Your data is never used to train, fine-tune or improve any AI model, ours or a third party's. Models run on Amazon Bedrock within your geography (EU or US). Agents never bypass your permissions, nothing they prepare takes effect without a user's confirmation, admins can switch any agent off at any time, and every AI interaction is logged.

Yes. Independent white-box penetration tests every year since 2022, by specialized firms (Vaadata, A-Lign). Our 2026 test focused on our AI agents and MCP server. Reports and remediation plans are available on request in our Trust Center. Between pentests, we run continuous vulnerability management with strict remediation deadlines, monitoring and annual control self-assessments.

Yes. SAML 2.0 SSO is available on the Scale plan, alongside Google sign-in. Your identity provider handles authentication; Qobra never stores your credentials.

We follow a documented incident response process, publish service status at status.qobra.co, and notify affected customers within 24 hours of identifying a data breach.